
Our Services
Integrated Security
Protecting your information, reputation, assets, and people is a key leadership responsibility.
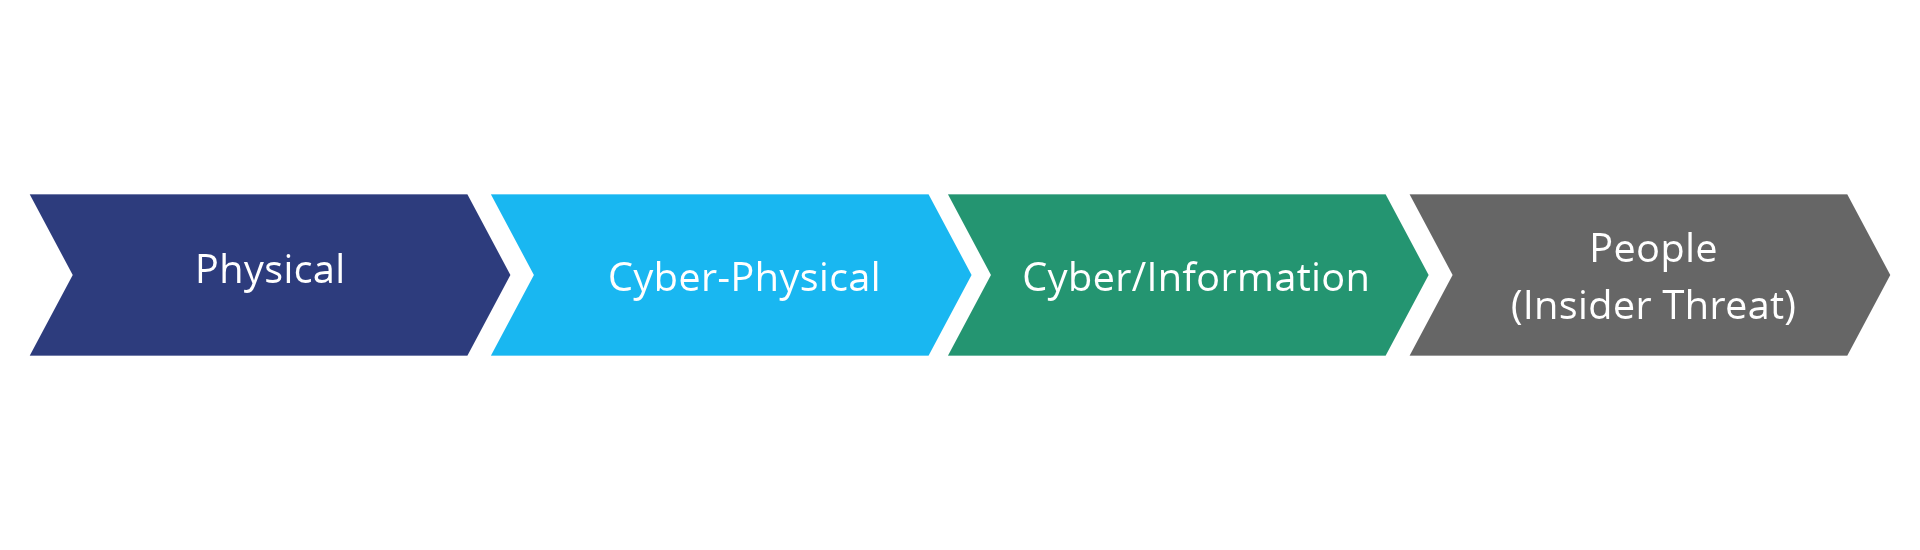
With the increasing complexity of business and government, it’s critical that security takes an integrated approach. This way you never miss a piece of the puzzle (effectiveness) and implement only the right security controls (efficiency).
Our Services Structure
Our integrated approach steps beyond the standard siloed security solutions in order to address our clients’ risks and issues holistically.
More often than not, the security challenges our clients face are multi-faceted and span multiple security domains. Anchoram’s Integrated Security Services team brings a multidisciplinary perspective to every security engagement. We achieve this through cross-collaboration between our experts in physical security, personnel security, cyber security, OT security, and fraud prevention.
Trusted by clients in many industries
Integrated Security Services

Anchoram's Crisis Management and Resilience Services help public and private sector organisations establish, assess and strengthen their crisis management, emergency response, business continuity and disaster recovery capabilities.

Anchoram assists organisations throughout the DISP lifecycle, from initial eligibility and readiness assessments through to security framework development, control implementation, application preparation, assessment support and ongoing compliance management.

Anchoram's Security Officer as a Service (SOaaS) provides a flexible, scalable and cost-effective solution through access to experienced protective security practitioners who can support the establishment, operation and continuous improvement of an organisation's Defence security management capability.

Anchoram provides an integrated, risk-based approach covering the interconnected disciplines of physical security, personnel security, information security, technology security, organisational resilience and security culture.
Anchoram's Protective Security Strategy Services assist public and private sector organisations to develop, review and implement comprehensive protective security strategies aligned with their business objectives, risk appetite, operating environments and regulatory obligations.
A well-defined Cyber Security Strategy is essential for organisations seeking to protect their critical information assets, manage evolving cyber threats, strengthen operational resilience…
An effective Cyber Security Strategy is essential for protecting an organisation's critical information assets, managing evolving cyber threats, meeting regulatory obligations, and supporting business objectives.
A maturity assessment is designed to enable organisations to identify and understand their key business risks and cyberthreat exposures and establish a baseline on where their current cyber security capabilities stand.
Anchoram's capabilities in this area range from helping you define the appropriate risk management framework and methodologies to utilising an existing organisational framework to assess cyber risks.
Operational Technology (OT) environments are increasingly exposed to sophisticated cyber threats as industrial control systems become more interconnected with enterprise IT networks, cloud…
Anchoram's AI Threat Modelling and Risk Management Services help organisations identify, assess, prioritise and mitigate cybersecurity threats and operational risks associated with the…
Insider risks can arise from employees, contractors, privileged users, third-party service providers and other trusted individuals who have legitimate access to organisational systems, information and assets.
This service is designed to systematically identify and evaluate security threats emanating from human vector, this could include employees, contractors and other business partners.
Our Security Architecture Development service assists organisations in designing and establishing a robust, scalable, and risk-aligned security architecture that protects critical business…
Our Cyber Security Architecture Review service provides organisations with an independent assessment of their existing security architecture to determine its effectiveness, resilience, and…
Identity and Access Management (IAM) helps to anticipate the threats associated with user identity and access to your systems and networks.
IAM is not a new concept, typically organisations have invested in multiple tools and technologies over the years.
Effective Identity and Access Management (IAM) implementation requires more than deploying technology.
Modern applications run on web platforms and APIs, and that is exactly where attackers focus their efforts.
Mobile applications are one of the fastest growing attack surfaces in the modern threat landscape.
Your network and infrastructure are the backbone of your organisation.
Artificial intelligence is being embedded into products, workflows and decision making processes faster than security practices can keep up.
Cloud environments offer enormous flexibility and scale but they also introduce a set of security risks that are easy to overlook and expensive to deal with after the fact.
Developing secure software is fundamental to protecting the users of our clients' products.Our Secure Software Review service provides organisations with a comprehensive assessment of…
Our Vulnerability Assessment and Research service helps organisations proactively identify, analyse, validate and prioritise security vulnerabilities across their technology environments…
Our Cyber Incident Response Simulation service helps organisations evaluate and strengthen their ability to detect, respond to, contain and recover from cyber security incidents through realistic, scenario-based exercises.
Red teaming operations are the best way to comprehensively test and refine your ability to sustain key operations during a security event.
Our Purple Team Operations service provides a collaborative, intelligence-led approach to strengthening an organisation’s cyber security detection, prevention and response capabilities by…
Our Attack Path Management service helps organisations proactively identify, analyse, prioritise and remediate potential cyberattack pathways that adversaries could exploit to compromise…
Our Security Operations Centre (SOC) Design and Establishment service helps organisations design, implement and operationalise a fit-for-purpose security operations capability to…
Our Detection as Code (DaC) service helps organisations design, develop, implement and continuously improve cyber threat detection capabilities using software engineering principles, automation and AI-assisted analytics.
Our Continuous Security Monitoring and Use Case Development service helps organisations strengthen their cyber threat detection, monitoring and response capabilities through the systematic…
Organisations frequently invest in advanced security platforms but lack the specialist technical capabilities required to integrate, configure and operationalise these solutions effectively.
Deploying security monitoring technologies does not necessarily mean an organisation can reliably identify and respond to cyber threats.
Our Security Operations Center (SOC) capability assessment offering is designed to provide a comprehensive assessment of the people, process, and technology aspects of an organisation’s SOC.
Cyber security incidents can trigger complex regulatory, legal and contractual obligations that require organisations to act quickly, accurately and transparently.
Following the detection of a cybersecurity incident, organisations can face significant challenges in analysing large volumes of security alerts, identifying malicious activity…
Cyber incidents can rapidly escalate into significant operational, financial, regulatory and reputational challenges.
Our Information Security Registered Assessors Program (IRAP) Assessment service helps Australian Government agencies, critical infrastructure operators, cloud service providers and other…
Anchoram's IRAP Readiness Assistance and Advisory service helps organisations prepare for formal assessments under the Australian Signals Directorate's (ASD) Infosec Registered Assessors Program (IRAP).
Anchoram's IRAP Documentation Support service assists organisations in developing, reviewing and maintaining the security documentation, control records and supporting evidence required to…
Anchoram's CPS 234 Information Security Assessment service provides organisations regulated by the Australian Prudential Regulation Authority (APRA) with an independent, evidence-based…
Anchoram's ISO/IEC 27001 Readiness Assessment service helps organisations evaluate their preparedness for ISO/IEC 27001 certification by assessing the design, implementation and operational…
Anchoram's ISO 27001 Implementation and Audit Readiness Support service assists organisations in designing, establishing, implementing and operationalising an Information Security…
Anchoram's Payment Card Industry Data Security Standard (PCI DSS) Implementation and Audit Readiness Support service helps organisations establish, implement, strengthen and validate…
Partners and Memberships





Let’s discuss your mission and how we can assist!
We are available for detailed discussion regarding your specific project requirements.
